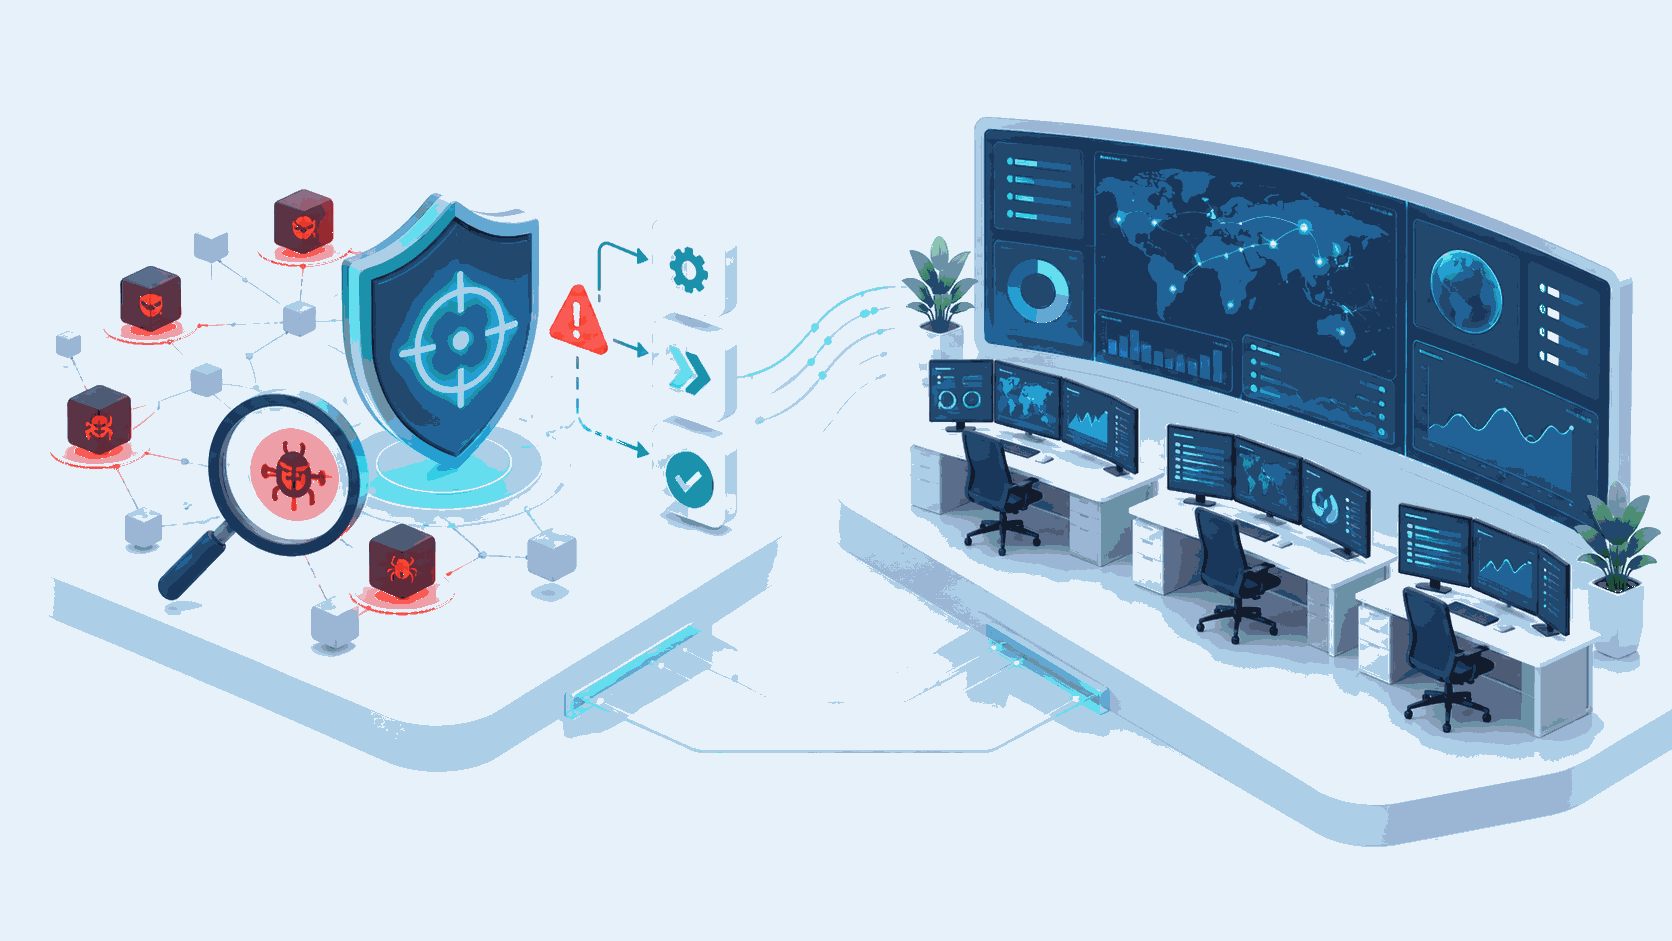
MDR stands for " managed detection and response." It is a service in which a provider monitors the security alerts generated by your XDR solution, sorts and analyzes them, and takes action on your behalf when a threat is confirmed.
The most common misconception is about what MDR replaces. It does not replace your security solution; rather, it leverages it. Implementing an MDR service is not the same as deploying an XDR: it involves setting up the managed service on top of an XDR that is either already installed or will be installed. Without a detection tool, an MDR has nothing to monitor.
What an MDR Service Covers
The standard scope covers four environments:
- workstations and servers, via the EPP or XDR agent;
- messaging and collaboration tools;
- identities, that is, accounts and authentication;
- mobile devices, when they are enrolled.
Across these four areas, the service provider does more than just issue warnings. It isolates a compromised system, blocks an account, and deletes a malicious file. This is the “response” part of the acronym, and it’s what sets an MDR apart from a monitoring service that would simply send you an alert at 3:00 a.m. and leave you to figure it out on your own.
What an MDR service does not cover
This is the question you should ask before signing, and it’s rarely addressed. An MDR provider only sees what its XDR solution reports back to it. This results in three blind spots.
If it doesn't have an agent, it doesn't exist. A machine on which the agent hasn't been deployed, a server overlooked during a migration, a workstation loaned to an outside contractor—they are invisible to the department.
Anything that doesn't go through the agent isn't detected either. An attack that passes through the firewall without ever touching an affected workstation goes undetected. The same applies to certain techniques that target Active Directory.
There are no custom rules. An MDR applies the detection rules defined by the XDR provider. If your risk is specific—for example, abnormal use of your ERP system or unusual access to a business application—it will not be detected because there is no written rule for that scenario.
On top of that, there’s the issue of traceability. An MDR retains logs for as long as the XDR solution does—which isn’t very long. If you need to demonstrate what happened six months ago—for an audit, for an insurer, or under NIS2—you won’t have that information.
MDR, Managed SOC, and MSSP: Three Different Things
These three terms are often used interchangeably. They are not synonyms.
MDR is a tool-based service with a defined scope and rapid deployment.
A managed SOC is a security operations center operated on your behalf. It collects logs from multiple sources into a SIEM, correlates them, detects scenarios that a single tool would miss, and allows you to create rules tailored to your specific context.
MSSP, which stands for managed security service provider, is not a service but a category of service provider. An MSSP may offer MDR, managed SOC, firewall management, or compliance services. The term describes who is selling to you, not what you are buying. We discuss this point in detail in our article on managed SOC and cybersecurity outsourcing for small and medium-sized businesses.
The comparison, scope by scope
| Criterion | LOL | Managed SOC |
|---|---|---|
| Workstations and Servers (EPP/XDR) | Included | Included |
| Messaging and Collaboration | Included | Included |
| Identities (Entra ID) | Included | Included |
| Server logs, Active Directory, DNS, DHCP | No | Included |
| Front-end firewall logs, Wi-Fi, backups | No | Included |
| Microsoft 365 Services (Exchange, SharePoint, OneDrive, Teams) | No | Included |
| Remedial Actions | Jobs, Messaging, Identities | Mail servers, messaging, identities, Active Directory, firewalls |
| Custom Detection Rules | No | Yes |
| Newspaper Preservation | No dedicated retention; retention is limited to that of the XDR solution | Yes, duration to be determined |
| Commissioning Timeframe | Short | Long; framing required |
| Dependency | Limited to the scope of the XDR solution | Open to any source |
Microsoft 365 Business Premium: What You Already Have
Many French small and medium-sized businesses use Microsoft 365 Business Premium without knowing what the license covers in terms of security. It includes protection for endpoints and servers, email and collaboration, and identities. These are exactly the areas covered by a standard MDR. Mobile devices are covered if they are enrolled in Intune.
Neither network detection nor a proxy is included. And most importantly, the license gives you the tools, not the analysts. That’s exactly the gap that an MDR service fills: the technology has already been paid for, but there’s no one to review the data it reports and take action.
How Is an MDR Service Set Up?
The implementation process is short, and that is its main selling point compared to a SOC. It consists of four steps: a kickoff meeting, a workshop to assess the existing scope, the deployment of the service tools, and finally, validation, accompanied by a quick audit of the existing XDR solution.
This last point is not just a formality. The audit verifies that the agent is actually deployed everywhere and configured correctly. It is this that determines the value of everything else: monitoring a fleet that is only half-equipped is like watching over a house where you’ve forgotten two windows.
MDR or Managed SOC: How to Decide
Three questions are all it takes.
Is your risk standard or specific? If your sensitive assets are your workstations, email, and accounts, MDR meets your needs. If you operate a business application, an industrial environment, or data whose compromise would entail a specific cost, you need a SOC capable of creating rules for them.
Do you have a traceability requirement? NIS2, DORA, ISO 27001, a major client, an insurer: whenever you need to provide evidence, log retention becomes the deciding factor—and the MDR does not cover it.
How much time do you have? An MDR can be deployed quickly. A SOC requires configuration, connectors, and correlation rules. If the deadline is an insurance renegotiation in six weeks, the answer is the MDR.
One final point, which is less pleasant to admit: a properly operated MDR provides better protection than a poorly managed SOC whose alerts no one reads. The scope of the system matters less than the actual ability to respond to what is detected.
IT Systèmes operates both services from France. Details on coverage, analysts, and reporting can be found on our Managed SOC and MDR page. The preventive aspect—including patches and hardening—falls under security maintenance, which is a separate but complementary initiative.
Frequently asked questions
What does LOL mean?
MDR stands for managed detection and response. A service provider monitors the alerts generated by your security solution, analyzes them, and performs remediation actions on your behalf.
What is the difference between EDR, XDR, and MDR?
EDR and XDR are software solutions: they detect threats. MDR is a service: people analyze the findings of these software solutions. Buying an XDR without MDR is like installing an alarm with no one to answer it when it goes off.
Does MDR replace antivirus software?
No. On the contrary, it assumes that a security solution is already deployed on the workstations and servers, since that solution generates the signals to be monitored.
Do you need MDR if you already have Microsoft 365 Business Premium?
The license provides detection tools for endpoints, email, and identities. It does not include analysts or out-of-hours alert support. MDR adds this human layer to technology you’re already paying for.
How much does an MDR service cost?
The price depends on the number of workstations and servers being monitored, as well as the environments included in the scope. It is calculated based on a quote, with a one-time setup fee separate from the recurring fee.
Is the MDR sufficient to ensure compliance with NIS2?
It covers detection and response, but not log retention, which is a key consideration for demonstrating what happened during an incident. A managed SOC with log retention is more suitable when evidence is required.